Binance hack findings show attackers targeted the exchange’s engineers for months before the October 29 theft. Attackers used stolen credentials to reach the internal wallet signing service. The access enabled transfers outside the exchange’s normal withdrawal process.
The crypto exchange put the loss at about $6.34 billion. The November 3 report describes three affected engineers, using the anonymous labels A, B, and C.
Malware in Binance Hack Compromised Devices
In June, Engineer A downloaded a tampered Homebrew installer while setting up an AI coding tool. The exchange replaced his device and rotated credentials after detecting the breach.
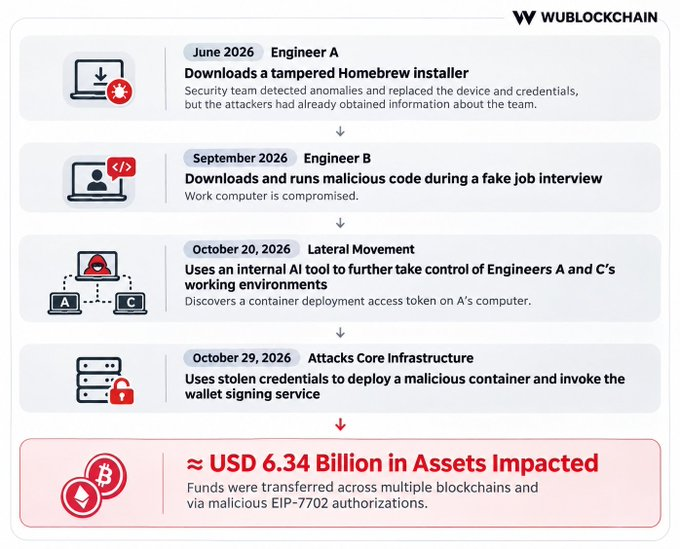
A fake job interview linked to the Binance hack targeted Engineer B in September. He downloaded a coding assignment containing a malicious repository.
Stolen Credentials Enabled the Attack
On October 20, attackers used that device and an internal AI tool to compromise A and C. They also found a container deployment token on A’s computer. Nine days later, the group accessed C’s computer and used credentials stolen from A. It deployed a container and ran a malicious script to launch the theft.
Separately, a commentator blamed the Binance hack on a malicious Google advertisement. The preliminary findings describe an altered installer and an infected repository. They do not confirm that an advertisement led to the breach.
Related: GitBook AI Attack Exposes API Secrets, Triggers Urgent Security Response
Disclaimer: The information presented in this article is for informational and educational purposes only. The article does not constitute financial advice or advice of any kind. Coin Edition is not responsible for any losses incurred as a result of the utilization of content, products, or services mentioned. Readers are advised to exercise caution before taking any action related to the company.