- North Korean hacker WaterPlum reportedly stole $10.7 million in crypto through fake job offers.
- Developers, IT professionals, and Web3 workers are among the main targets.
- Job seekers can reduce risks by verifying recruiters and avoiding unknown files.
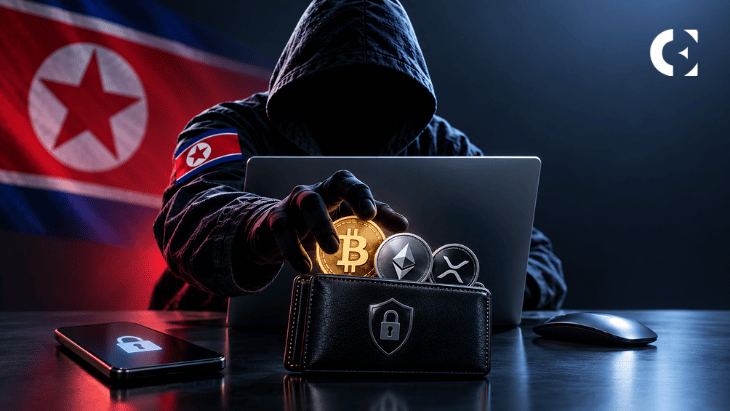
North Korean hackers are now using fake crypto job offers, a technique that has become increasingly common in crypto-related hacks, to target developers and Web3 professionals. They are reportedly posing as recruiters, luring developers and professionals into downloading malicious files. This has led to the loss of millions of dollars in crypto, affecting thousands of devices.
North Korean Hackers Use Fake Crypto Job Offers to Steal Assets
According to the latest reports, North Korean hackers called Waterplum are faking job offers to steal millions in crypto from people working in the blockchain sector. Disguising themselves as recruiting agents of credible organizations, the attackers approach developers or other individuals by promising them great opportunities.
It is reported that the hackers have managed to steal up to $10.7 million worth of crypto. From December 2025 through July 2026, the WaterPlum attack has compromised roughly 30,000 computers in 100 countries, taking out money or information from more than 7,000 crypto wallets.
While the recruiting process is ongoing, the attackers make candidates install some code, execute some program, or open some file. But these procedures, which may look like a usual hiring assignment, could ultimately turn into an attack.
As the files contain malware, the applicants may unknowingly download it, giving attackers access to the information stored on the device. The data includes browser details, passwords, and crypto wallet info. Thus, attackers could access the individual’s personal information and steal their digital assets.
Who Is Being Targeted by Fake Recruiters?
Notably, North Korean hackers target people in the crypto industry, especially developers, software engineers, IT professionals, and Web3 workers, as these professionals’ work often involves handling code, digital assets, and sensitive information. A joint advisory from Japan, Germany, Australia, and the US. Authorities stated, “The primary targets were individual web designers, engineers, and specialists in cryptocurrency, blockchain, and Web3 technologies.”
Thus, job seekers seeking remote or freelance opportunities could be the first target of the hackers. This is mainly because they could be targeted through social media, job platforms, and messaging apps.
Can a Fake Coding Test Steal Your Crypto?
It is important to note that a fake coding test containing malicious software can put a crypto wallet at risk. While it may initially look like a normal coding task or interview file, attackers can use the fake crypto jobs to gain access to the individual’s device and thus their personal info. If they gain control over the crypto wallet, they could easily steal the individual’s digital asset holdings.
What Should You Do After Downloading a Suspicious File?
If an individual downloads a suspicious file, unfortunately, the first thing to do is to avoid opening it. But if you have already opened it, things become riskier. However, you can avoid risks to an extent by disconnecting the device from the internet immediately to limit further access.
Crypto users should also avoid logging into wallets, exchanges, or other important accounts from the infected devices. They can use other devices to change important passwords and enable two-step verification. It is better to move funds from an infected wallet to a new secure wallet. If anyone contacts crypto users claiming to be a recruiter or security expert, they should remain vigilant and should not share seed phrases or private keys.
How to Spot a Fake Crypto Job Offer?
Significantly, job seekers should be careful when receiving a job offer. The main thing is to verify if the company is real and whether the position is listed officially. Next, the applicant should check the recruiter’s profile and make sure that it is authentic. The offer could be suspicious if it is not sent via an official email address. Unusually high salary packages and other perks could also be seen as a warning sign.
When the interview process begins, if the interviewer asks you to download unknown software or code, it could be a sign of a fake crypto job offer. An authentic interviewer will never ask for wallet details, private keys, or seed phrases.
(adsbygoogle = window.adsbygoogle || []).push({});What This Means for Crypto Investors and Developers
The WaterPlum hacking incidents highlight the importance of vigilance and caution while handling job offers. Particularly for people in the crypto space, job offers and interviews need to be handled with caution, as similar hacks are now growing. If a device is compromised during an interview, the attacker can steal the applicant’s wallet information, passwords, digital assets, and other sensitive data.
Related: North Korea-Linked Hackers Used Fake Jobs to Steal Crypto From IT Workers
Disclaimer: The information presented in this article is for informational and educational purposes only. The article does not constitute financial advice or advice of any kind. Coin Edition is not responsible for any losses incurred as a result of the utilization of content, products, or services mentioned. Readers are advised to exercise caution before taking any action related to the company.